Spoofed Email Address Scam

The following is based on an actual case, and shows you how scammers work. In this case not very successfully, but I will come on to that in a moment. 

Scam Plot

A message arrives in your inbox which appears to have come from your account. So it is from you to you. That implies someone may have access to your email account. Something that is likely to generate a panic response, which is exactly what they are hoping for. See below for an example. Click on the image to see a larger version of it. 

For most of you though you will not see this message

Why?  If your email is hosted with me, or with Outlook.com, then you will never see this message because of something called SPF (Server Policy Framework). It is a list of legitimate sending servers which is located in your DNS settings. It is there so that any email system receiving a message from your email sending server can verify that the message actually came from your server and not from somewhere else. It is a basic test, and if it fails the email is discarded. It is handled on the receiving server.

If you do not have an SPF policy set up, then you will see the message as intended by the sender.

What the Spammer Scammer did

In this case there was a trail of evidence, because the actual message that arrived was a bounce back message, and then a reply from the actual server it came from.

It appears that the individual behind this, took over a server in a Canadian hosting company. Either used a special program to do this or wrote a script to do this. The script probably had a list of target email addresses scraped from websites. It formatted the email and populated the sending email address and the destination email address as the same address and then sent out 625 of them. We know it was 625 because the following happened.

  • Email is received and then some automated tests are carried out
  • Email is rejected because it did not come from your sending server, there was not a match, therefore it is a “spoofed email”.
  • A message is sent back to the actual sending server. At this point no email has appeared in your inbox, or in junk mail, this is all happening automatically.
  • The message arrives at the originating server, but there is no corresponding email account at the sending server, and the server replies with an error message back to your inbox.
  • Because it is an error message you get the error message and original payload. This is called a Bounceback message, it is sent to warn you of problems with email.

The bounceback message

This message was created automatically by mail delivery software.

A message that you sent could not be delivered to one or more of its
recipients. This is a permanent error. The following address(es) failed:

  info@xxxxxxxxxxxxxxxx.org.uk
    Domain tidunglagoon.com has exceeded the max emails per hour (625/500 (125%)) allowed.  Message discarded.

Reporting-MTA: dns; sng123.hawkhost.com

Action: failed

 
Here we can see where it originated from, a mail server for tidunglagoon.com. We can also see from the message that 625 emails have been sent, so this was not the only one.

The Email Header

Not shown here, but viewed by me is the email header. All emails include a header which is not normally visible. But it is present on all emails. It contains information about the source of the email and the destination. It also contains information about any tests that have been subjected to the message, particularly around spam scores. 

This is the first place to look if you get a dodgy email. It is also important if you need to share the email with a third party for analysis. 

There will always be a link or something traceable

In all of the various spoofed emails and scams there will always be a link to something. In this case there is a reference to a digital wallet so the person can receive a bit coin. I do not think you can trace that to an individual, so it is a great way of hiding. Sometimes there is an email address, or a hidden link to a website. While not impossible, those are fairly easy to hide behind too. 

What if you receive something like this?

Firstly do not panic. The sender wants you to panic, that is why these emails are constructed like this. The first task is to move the email to a special folder and leave it there. Do not click on anything in the email or send any reply. Also do not download any hidden images in the email because this confirms someone has read it. 

Calmly read through it and check to see if it is generic (could be applied to anyone) or specific to you. Chances are it is generic. If you are not sure about it, contact me and tell me about it, but do not send it to me. It is highly likely if you send it to me on my usual email address it will be detected and sent straight to my junk mail folder, so just let me know you have a problem you need me to check. 

What I will want to look at is the header in the email as well as the email contents, which is why you should park it somewhere safe and not delete it. 


Self directing spam to a spam folder!

We are all subject to spam messages, and sometimes they can be a real pain. There are various mechanisms for reducing it, the more sophisticated methods I use require a match between some text and an image. 

However if a human is behind sending spam, then they can defeat these systems and send it anyway. 

During an idle moment, I started think about it a bit more. 

If it is a human sending spam messages, then it is likely that they do not get paid much, and probably do not pay too much attention to what they are sending. I can tell this by looking at some of the messages that come in which have letters for example where telephone numbers should be. Or perhaps the systems are automated and have a human standing by when a problem occurs. 

Either way, I have also noted that if a choice is already made in a form, then the default choice is often used. So what happens if the default selection is “I send Spam“?  So I tried it. 

In the image you can see that there is now a selection for the subject line of the message. The default setting is “I send spam”. If a bot or bored human sends a message they will not change that setting.  Anyone genuinely wishing to contact the website will make a selection other than “I send spam”

… And here is the first candidate through this form. It is a spam message and they have not changed the subject line. So if this theory holds up I can now create a filter in my email box, that redirects the suspect message into a folder for messages that have “I send spam” in the subject line. 

The filter above will detect any messages coming into this mail box which contains the precise text “I send spam” on the subject line, and redirect it to a special folder called Spam Suspects.

About this approach

It is experimental, but looking promising.

Pros:

  • It should trap spammers who are either bots, human, bots supported by humans, people that are not paying attention.
  • With the default subject line the message can be accurately detected and sent to a special folder.
  • The inbox should be more clear of spam than it was before.

Cons:

  • A real enquirer not paying attention might also fall for it.
  • You still have to check the spam suspects folder and clear it out from time to time in case there is something important in there.

Your Website has been hacked….. send bit coins.

There is a well documented scam going around where you will receive a message which tells you your website has been hacked and they have all of your data, and data from your clients and they are going to contact everyone and sell the data and cause you a load of grief. (I have paraphrased that to keep it short). If you get anything like that please do the following:

1). Don’t panic

2). Send a copy of it to me

3). Wait until you hear back from me

Do not pay anyone anything, or engage in a conversation. The language including grammatical errors are recorded in multiple places on the web. It is a well known scam. Another one which is designed to instil panic in the recipient. 

While I am on the subject there is a second one which claims to have taken over the camera on your computer and has images of you in compromising situations (I will leave that to your imagination!), that one is another scam. I have not seen it recently, but what goes around comes around eventually. 

Both messages will come from a non traceable source, and both are asking you to deposit bit coins in an account.

Another Phishing Scam – You may be targeted

It has just been brought to my attention that there is a phishing scam going on where people who have websites at 20i.com (I have your a reseller account here) are being sent phishing emails. It works like this:

The hacker has done some research based on name servers and then identified the websites that are hosted at a data centre. They then visit the website and scrape an email from it. They then take a screen shot of a legitimate page from the parent hosting company and attach that into the body of a an email.  

Fortunately none of you receive any emails from 20i.com directly, so hopefully your suspicions will be raised immediately. However it would be possible for me to automate the accounting side of my reseller package and you would receive emails like this. I have just never bothered to set it up. 

In the image below I shown the email which someone had kindly detected and flagged to me. I recognised it immediately as a 20i message. You would never receive one of these unless you had your own account with them. 

I have also placed my cursor over the image so you can see where the link goes to. You can see immediately it does not go to 20i.com, it goes to a server in Spain. 

This is a classic Phishing Scam. What they are after is maybe payment, or a username and password to log into the system. Either way it is a criminal act. 

Ways to detect these types of scams

When you look at the image above, it does look genuine on first glancing at it and not looking closely. It is actually based on a real message that they send out, but I am the only one that might get one, not you. 

There is a glaring error on the first line where they have adapted the message. “…. will expire within the next days.”  The actual number of days is missing. That is so they can create a reusable block of text for anyone. There are also special characters embedded in it which do not display correctly and if you look at the punctuation it is incorrectly spaced as well. 

Bottom line

If you receive a message and it does not look right, it probably is not right. The general give away is not much context and a link, or a lot of credible context, but the link is through an image. You can always find where a link goes to in most mail programs by placing your cursor on top of the link but not clicking.  In this case you would be passing information to a hacked server at http://……clinicapodologiabarcelona.es  (I suspect a foot clinic in Barcelona). 

Invoices relating to your services

You will only ever receive a message directly from me, it will not contain any links for you to login somewhere else. You would never receive a message from the hosting provider I use directly unless you had an account with them. 

Please remain vigilant, and drop me a line if you are unsure about anything, I would rather spend time replying than see anyone caught out, there is a lot of this going on right now. 


Beware of the peaks!

For much of the past month I have been working my way around sites and making sure the sites are updating correctly. In some cases they have not been doing this without additional input. I have not got to the bottom of why, some of it is related to the Divi template. I spent a very tortuous 2 days seeking support to find out why. It would have been more productive watching paint dry. 

However I digress, I looked at around 70 of the sites I am hosting. I had to make changes to them to get the last version of WordPress to manage the updates. After I have done this the sites should in theory look after themselves. 

In the dashboard of most sites is a Google Analytics summary of the last 30 days of activity on your site. I noted the image below which has a strange peak in it on one of the sites. 

This is not normal

Then I found another one

And another one

And another one

Unravelling the thread

I found five in around 70 sites, so it was not everywhere. But what is it? I chose one site and decided to check Google Analytics to see what it recorded.  The peak in most cases occurred over a 5 minute period when allegedly around 350+ people from around the world decided to visit your website at 9am in the morning. And I do mean from around the world, not just in the UK. Any country in the image below that is a shade of blue, means people (allegedly) came from that country. 

The image on the left shows the top 31 countries and how many computers in each country.  Click on the image to see a larger version.  Not listed here, but I did check, looking at Russia countrywide, the visits did not come from one computer, but came from many across Russia.

What is going on?

Given the attack which is still going on some 4 weeks after I was notified on another site, I am very conscious of how long that took to sort out. I checked in with the hosting company to ask about these and what they thought they were. I did not get a straight answer, other than any attack will be handled by special measures in the hosting and the site will continue to work despite this.

It is unlikely that these sites were affected in any way, the visits in this case were no different to UK based visitors. The only difference is they came from everywhere in a very short period of time, apparently altogether or in quick succession.

Speculation

A few years ago I witnessed an attack on one of my sites while with another hosting company. I documented it at the time in this site. The site in this case had a protection mechanism built in that if there were too many visitors arriving at once, or trying to log in, they delayed any further activity from that IP address. As soon as one was blocked another one started. When that was blocked another one started, and they skipped all around the world in a few minutes.

The site was not taken down, but this is basically known as a DDoS or Distributed Denial of Service attack. The expectation being that if enough computers hit your site it will consume the server resources and your site will grind to a halt.


Click on the image to see a larger version

BOT Network

It is highly likely that I was witnessing a Bot network which is a set of compromised servers from around the world controlled by one central resource and they were testing it. When I last came across this I had all of the IP addresses of the computers, and could do a geo location search and also identify the owners of the computers (if they were a server for example). In many cases they were corporate servers owned by respectable companies that probably had no idea that there were additional processes running off of their computers. 

The system might be targeted at some point on a corporate server and financial demands made to turn it off. 

Things for you to think about

If you see a massive peak in your statistics that you cannot account for, let me know ASAP. I will look into it. If you have one of these it means your statistics for that period are no longer valid. So do not use them in any promotional documentation. 

You may have seen in the past messages like “We checked your website and it was not getting many visitors pay us ££££ and we will increase the number of visitors to your site”  Well this is one way of doing it. It will not however generate any more business because the visitors are not real.  

I can selectively turn off countries from accessing your website and take some other measures with the hosting company if you see anything like this. 

However it should not really impact your website, or your existing visitors. If you are not sure about something; drop me a line. 

Captcha Solution for Contact Form 7

I have been using contact form 7 on many websites for the past few years. I have noticed that there are some anti spam measures which are being defeated by spam bots (computers that post spam into forms).

I am reluctant to use Google Captcha because I think that while it is undoubtedly effective, it also presents a barrier to some users, particularly elderly ones. I have also seen preferential treatment (aka easy access) when a user is using Chrome, but other browsers they may be stuck answering questions makes bypassing it frustrating to say the least.

I have just found Contact Form 7 Image Captcha by KC Computing (Kyle Charlton) which is very elegant, simple and works fine. It asks the user to click on an image which matches some text. A user has to complete this step before submitting the form.

If your site is using Contact Form 7, you can load this plugin into the library and then insert the following shortcode into the form: [cf7ic “toggle”]

If your website uses the form in a dark coloured panel, the formatting of the text may not work very well. To get around that problem you can add the following text into the CSS for your site. For Divi users this can be found on the Divi settings page at the bottom. There is a space to add CSS in there. It will change the selected text to yellow.


.captcha-image .cf7ic_instructions span {
color:yellow !important;
}

Dangerous Spam in Circulation

I subscribe to a number of websites that report on vulnerabilities and various scams as they emerge. One in particular caught my eye as we currently have at least one site under constant bombardment  (4 per minute for 8 days now) with a spam email that carries a highly suspicious link. In that case no damage has been done other than wasting a lot of my time. The sending VPN node is blocked (the actual sender is hidden from us) and the content of the email has been analysed and if any get through they are sent to a junk email folder.  The problem here is detecting it when it happens to minimise disruption. 

One such publication is called Hacker News. I get that daily, and there are all sorts of reports of problems in major systems. I want to bring your attention to just one of them. 

IcedID

There is a particular email circulating right now which will come most likely through your contact form, will look official and will advise you that are using images on your site which are subject to copyright. Practically speaking, while I know some organisations are not particularly careful where they pick images up from, I have only ever come across one legitimate case. 

The email carries an obfuscated link (you cannot tell where it is going to take you to) this is really the first warning sign. Never click on anything that does not look right particularly if it is an unsolicited email. In this case the email states that the link will lead to evidence of copyright infringement and you need to take action now or legal action will be taken against your organisation. This type of email is likely to panic someone into clicking on the link.  If you see anything like this relating to your website forward it to me and I will check it. 

If you do click on the link it will lead to downloading “IcedID” an information stealing malware. If you do not have strong security on your system with AV and Security software the download may not be detected. 

You can read about it here: Hackers Using Website’s Contact Forms to Deliver IcedID Malware (thehackernews.com)

Most junk email is easily identified, there are a few around that can scare people into taking action. Don’t become a victim of that. Send it to me, I will check it out for you. 

Case Study – Extreme Spam!

I had an email from one of my clients informing me that they had 4000 emails in their inbox which had suddenly appeared. There were more being added every minute. Typically this charity received 3 or 4 a week.

What happened?

It appeared that someone was directing spam messages through the website at a rate of 4 per minute. Analysis of the emails coming in was interesting. They all came in through a contact form which had several anti spam measures included which had been defeated. Perhaps this was their goal to write an automated program which defeated the forms anti spam measures and fill the inbox. Which is a sort of denial of service attack.

Every email was different. They allegedly came from different email addresses, and the payload in the message was also different. So spam filtering could not work on a sender address, or easily by looking for some keywords or domain names.

The message encouraged the viewer to click on an obfuscated link (the destination of the link is coded so you cannot tell where it is going to). The coding for each link was also different.

Meanwhile while looking at this the volume of emails had now hit 6000.  I had seen this once before, but I guess it happens regularly, because much spam traffic is automatically generated through forms.  The question was what to do?

Start by looking at the emails

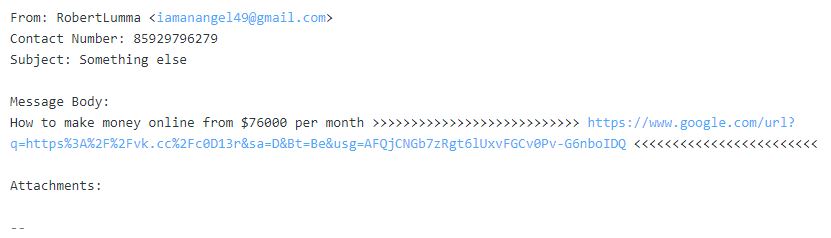
Each email had a couple of common elements in it. There was a brief message followed by a varying number of: >>>>>>>  then a web address (always different) and then a varying number of:  <<<<<<<.

If you look in your hosting, or through your webmail account you can set up filters for incoming mail. The filters work at a very detailed level per email account. I had not used them before.

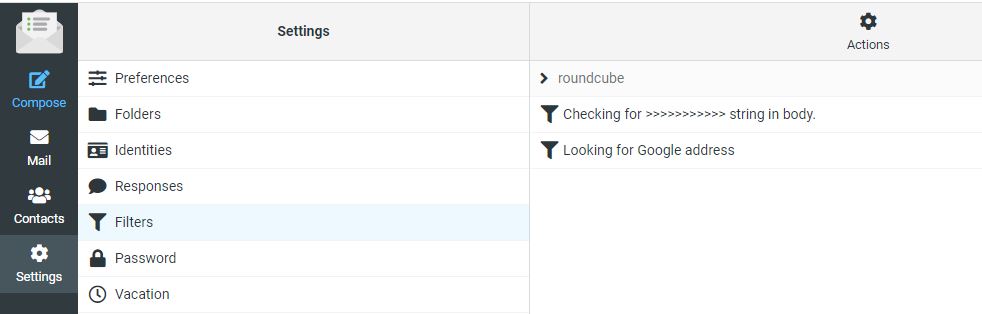
I logged into the email account via webmail and chose Settings and then Filters and set up a couple of filters.


In the example above you can see I have set two filters up. Lets look at them to see how they work, and what limitations they may present. 

Filter 1 Looking for this sequence “>>>>>>>>>>”

All of the email had two sequences of greater and less than symbols to draw the viewers attention to a web address they wanted you to click on. 

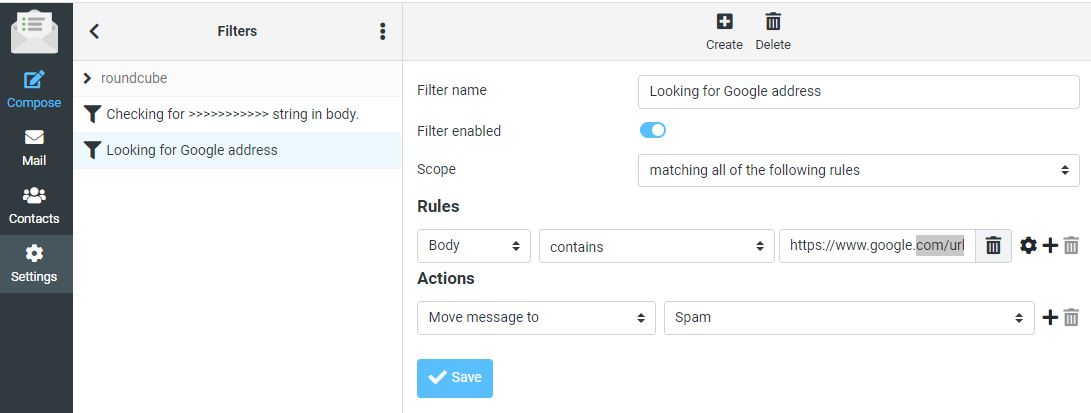
I set up a rule which says check all incoming email to this account and look in the body of the email. If you find “>>>>>>>>>>>>”  as a sequence in this email move the message to the Spam folder.  Here are the settings.

You can see from this layout that you could build a very complex filter and have lots of conditions that need to be met before deciding what to do with the email. I could have refined it further, but I was under pressure at the time to regain control of the account. So I created a second filter on the Web address in each message. 

Filter 2 Catching a web address

In this case all of the messages had a different email address. They all started as https://www.google.com/url?…..     followed by a series of random characters. This is a method of hiding the destination address. But because all of the messages contained this common sequence I could use it. Here is the second filter. 

What happens now?

With these two filters set up any messages coming into the inbox that contained either “>>>>>>>>>>” or more in a sequence OR a message carrying “https://www.google.com/url?” were now automatically sent to the spam folder.  While this might look like success it was not the whole story. 

Messages like the one below were now going into the spam folder, all of them were being trapped. However the computer was still hitting the website 4 x a minute.  While email was now usable, the problem had not gone away. 

The hosting company keeps a log of activity on the website. It is not an endless log, but it will show you maybe the last 3-4 hrs of activity. I decided to take a look there. This would tell me if it was a network of computers from around the world (which has happened before too), or a single computer running some sort of automated program. 

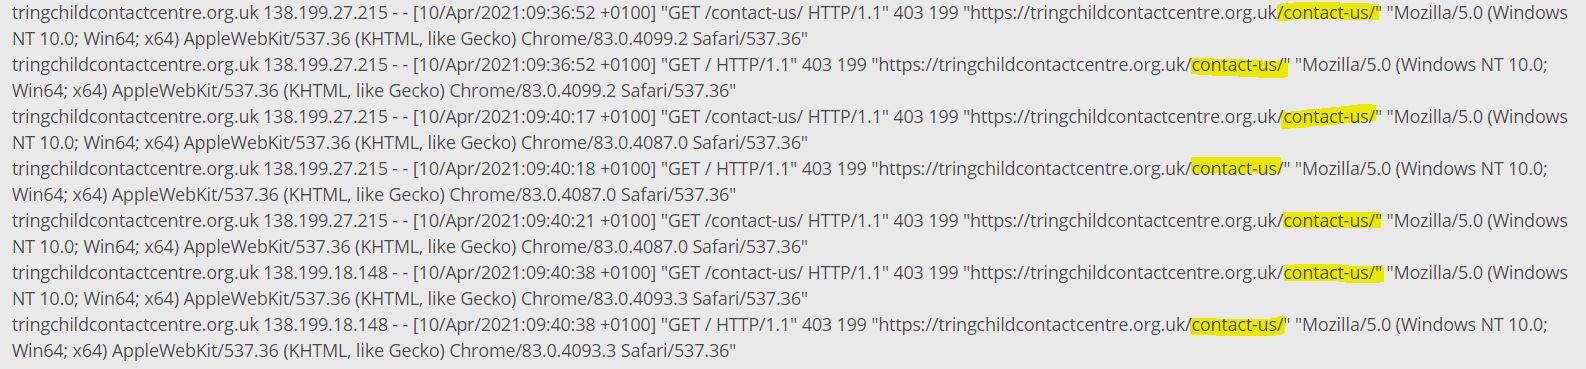
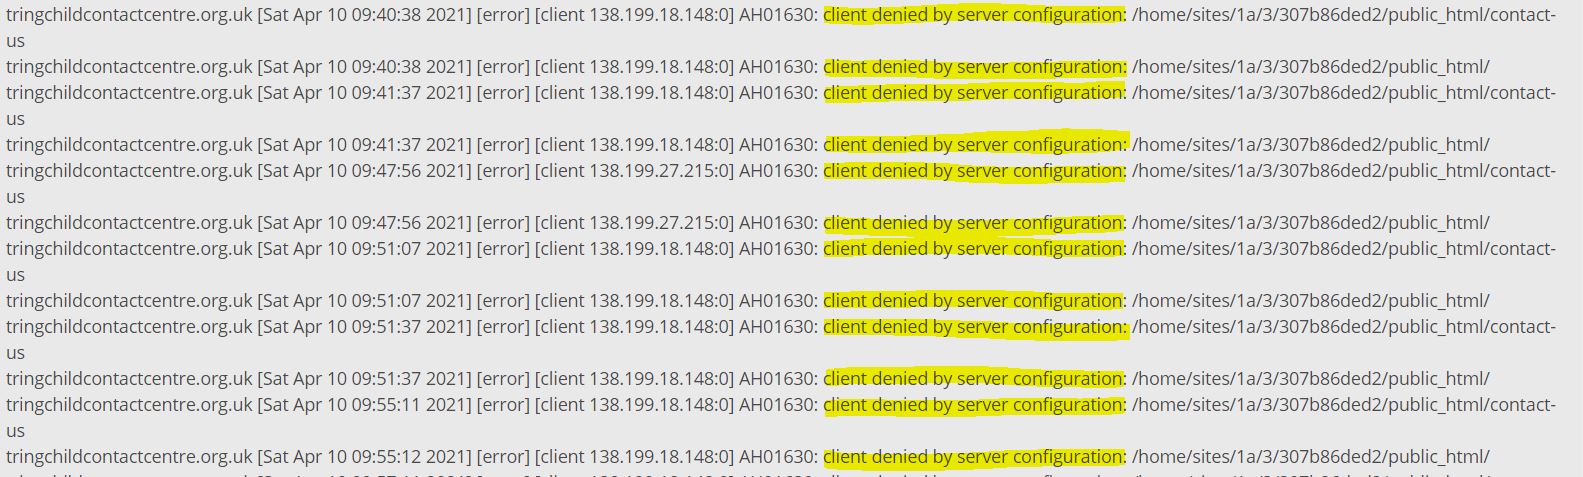
Here is an example log with an access to the contact form highlighted. 

The access log shows that something(s) are constantly accessing the contact us form on this website. The time stamps of the log show as high as 5 time per minute.  These accesses are coming from two sources: 138.199.27.215 and 138.199.18.148.  When I did this the first time through I only saw one IP address. 

In the hosting you can block accesses to the website by country, by IP address or by IP address range. The country block is not fool proof because people can appear through IP addresses which are not listed, or pop up through a VPN somewhere. 

Where is the spammer located?

Can I block by country?  I went to this website and entered the IP address to see what it came back with.  https://www.iplocation.net/  It came back with the following information:

This tells me several things. There are actually several entries from various databases, I have shown 3 here. It tells me the computer is located in France, in Paris at Ile-de-France. It also tells me that the service provider is a UK based company called Datacamp Limited.

Block France and then the whole world!

I next went back into the hosting and looked at the filtering options. This client only has clients local to their area, and certainly in the UK. So there is probably no need to have this website visible in other countries. At least for a short period. So I first blocked France, then blocked everywhere apart from the UK.

This action did not immediately work. Possibly because the block is not instant. The logs showed continuous accesses to the site. There is another reason, just speculation; the account was being served through a CDN (Content Delivery Network) and it might take some time for the content to age and be replaced. I tried clearing the server side cache but it had no effect. So what now?

Block by IP address

As I knew the IP address of the computer sending the messages into the website, it is possible to block based on the IP address which I did.

That stopped some of the accesses but then another IP address popped up. I have been here before, and traced a network of compromised servers around the world that were sending spam several years ago. The new address was 138.199.18.148. So there were either two computers, or more likely one computer with two ports attached to the internet. 

The second IP address is similar to the first (first two number are 138.199) and are also with the hosting company Datacamp Ltd. 

There is another type of block where you can block a series of IP addresses on the basis that hosting companies will acquire blocks of IP addresses which are in sequence. I set up a filter in the hosting which blocks 65,535 addresses all of which start with 138.199.

This blocks any computer working on this range of addresses:  138.199.0.0 to 138.199.255.255.  

Here are the blocks in the hosting control panel. 

In this case the entry 138.199.*   overrides the other two entries which were specific to two locations.

This prevents these computers from seeing the contact form. So if they cannot see it they cannot post data into it. The website is not visible to them.

There is a second log in the hosting which records errors. You can see that each time the automated computer attempts to access the form it receives a 403 response from the website which means “Forbidden”. Their access is denied.

At this point the automated spamming computer cannot reach the website and cannot send any messages through the contact form.  But it is still trying. It is still trying to do this 3 days later. Someone has left it on to keep attempting to hit this website.  So what else can you do?

Contact the Hosting Company

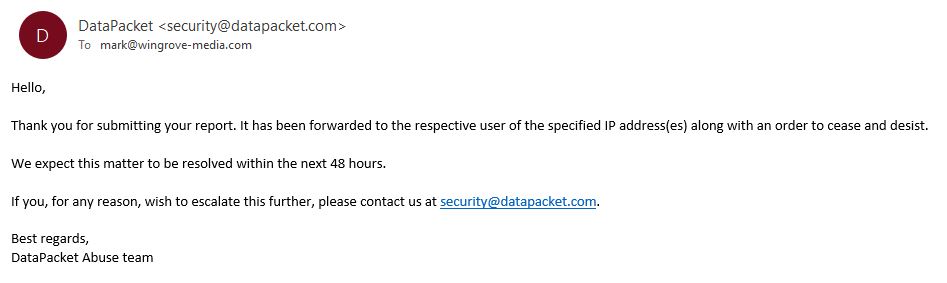
People connect to the internet through a service provider or hosting company. In this case I had strong evidence that the person doing this was accessing the internet through a connection provided by Datacamp Ltd. So I tried to reach out to Datacamp through their website: https://datacamp.co.uk/  The website has a single email address visible and a telephone number. I sent an email to datacamp@datacamp.co.uk to advise them of the problem and request that they shut down the connection. Nothing happened, no response. So then I phoned 020 3808 5949 and left my number. No reply.  I then did some searches on Datacamp Ltd and found that it is a parent company for CDN77. I went on that site and got on a chat with a representative of that company. They gave me another email address: abuse@datacamp.co.uk which finally did get a response. 


At the time of writing the offending computer in France is still trying to hit the website contact form. Tomorrow I will escalate it yet again. 

Whose fault is it?

It is unlikely that we will ever know who was behind this. There was probably no malice or directed attack at this particular charity other than they were testing something.  A similar case a few years ago involved around 20 computers that were around the world doing something similar. They were less sophisticated than this attack, because in this case it defeated some tests in a form. I also changed the tests by replacing some different questions and it was still able to defeat it.  I will look for some alternative methods to keep automated machines out. 

It may well be the case that the computer this process is running on is a highjacked server someone has taken over, or has infiltrated. The owner knows nothing about it, and the service provider has no relationship at all with the people behind the attack. We will never know. 

Sadly dealing with this type of thing is a fact of life. It goes on all of the time. But if it happens to you, we have some tools available in the hosting to minimise any loss of service. 

If anything else happens here, I will update this. 

Update 15/04/21

We are now a week later after this was first reported. The senders IP address has changed twice over the past week, but the messages continue. If it had not been detected, this account would now have 50,000 junk emails in it!

Over the course of the past 5 days I have contacted the service provider’s security team, and they have passed the message on to their customer. Their customer is a VPN provider. People use VPNs to hide their identity or the source of the message. The computer that is sending the messages is an unmanaged system in a data centre which is subcontracted out to their client. It is their client’s customers, or even their customer’s customers causing the problem. Nothing can be traced. Frustrating isn’t it? 

I have contacted Action Fraud, and it seems the only thing I can do short of taking a private legal action against the company under the Computer Misuse Act 1990 for denial of service. There is nothing anyone can do, even though this is obviously wrong. It is also outside of the area that OfCom is responsible for.   I have been advised to raise a case with Action Fraud which I will probably  with the amount of evidence I now have.  

Another Scam, how it works

I don’t know whether it still happens but there used to be a method for a hacker to steal your address book from your computer as a result of you clicking on a link in an email, or on a website. Once they have that, they can send out messages appearing to be you to the people in your address book asking for help. One of the clues it has happened is finding a copy of your address book on your desktop and wondering why it is there. 

The following is an example of a spoofed email address where someone substitutes another email address for their real email address and sends a message. In this case I have substituted the real email address for another one to retain privacy. 

The person whom this relates to, I know vaguely, they used to be a client several years ago. The hacker/ spammer in this case knows there is a relationship between me and the person whose address book he has acquired. But he does not know the depth of the relationship. 

I knew this was not real from the first email, because I have seen them before. As you can see, they wanted money, so I played along for a bit. 


Email 1. The Bait

I receive the message, recognise the email address and the person, but as you can see the message does not have any more info in. I suspect it is not real, but I respond anyway, note my response is also very short.  But note what has happened with the email address. It has changed from barnaby97@yahoo.co.uk to barnaby97@hotmail.com this confirms that someone was spoofing the real email address. Now all mail will go to an email account the hacker controls. 


Taking the Bait

Reel ’em in

Acknowledge the news

The response: Spelling out what they need….

It is easy to see how people can get pulled in by this type of scam.  If you ever get anything remotely like this, always pick up the phone and call them direct to check if the message is genuine. In this case, I could not send a message to the (original) email address in case it was compromised by the hacker. I did not have a telephone number I could use to call them independently. 

Take care, especially during these times where we are very dependent on electronic communications. 

Watch out for Boris & his friends

This Boris comes from the USSR and other states that have no interest in your website other than abusing it. This is a short case study on why it is wise to remain alert.

Invitation to make some changes

On a few sites where I know there is very little annual activity on the behalf of the website owners, I help out from time to time adding a message here and there. Typically this year it has related to coronavirus shut down/ reopening messages. I received a message from one of my clients and proceeded to make the changes yesterday.

On entering the website there was an exclamation mark next to a plugin warning me there was a problem. I investigated, it related to an SMTP plugin which is used to handle sending messages on behalf of the website. This is usually more reliable than sending via PHP the native method in WordPress. By using an SMTP plugin the website connects to an SMTP (outgoing mailserver) and sends the message out through an email account.

In this case it warned me that error messages had been returned from the mail server. It invited me to send a test message to check it. Which I did. The first attempt returned an error, the second attempt a few seconds later was successful, the third attempt returned an error.

What was happening?

I have been down this path a few times, and suspected that the hosting company was limiting messages coming through the mail box, probably because of spam like activity. I raised a ticket with the hosting company and asked them to check and verify.

They never answered the question but requested access to the website to see the fault for themselves. They missed key points in the questions I had raised to them, so I tried again.

Second time around they blamed the plugin for the problem claiming there were no error messages in the hosting relating to failed email attempts. (But still did not answer the question whether they were blocking it or not).  So I tried again.

On the third request they did find error messages in the email log which also mentioned suspected spamming activity through the contact form on this website.

Website Log

At this point I checked the log of website accesses to see if I could spot anything there. Sure enough something was probing the website 4 times a minute over less than a 2 second period. Humans do not work that fast, so it had to be a bot (computer program running on a compromised server somewhere).

All accesses were from this IP address: 5.188.210.4. Checking that IP address it turns out to a server in Russia. Probably a legitimate server that has been compromised by someone.

Why should you be concerned about this?

From the first time around 7 years ago now, when I started to turn on security monitoring and you could actually see beyond normal website usage, I was surprised to see the volume of illegitimate attempts to access websites.

One of the most common is sledgehammer approach password guessing routines which try to get into your website. 

In this case, something was probing the contact us page and attempting to use it to send spam.  It later turned out that the website owner had received 257 spam messages, but they had all been trapped in the email program they were using. 

Whatever it was trying to do, it was triggering a safety function in the hosting which was stopping or rate limiting messages from this website. So while it may have tried to send thousands of messages, only a few got out. BUT…. it also means that this Russian computer was hitting the website so hard, that it would have affected any legitimate messages coming in through the contact us page. 

When I did my test, it failed, then passed, and then failed for another 10 attempts. 

So, if your junk mail rises for any reason beyond a few messages a day, be suspicious. Someone may be targeting your website, and they may be impacting your website’s ability to send messages. Or said another way, your clients to reach you through your website. The main problem here is there is no warning given, no messages of failed delivery. 

How to fix it

In all of my cases, I work locally in the UK, the audience with a few exceptions are all UK based, and in most cases probably within 50 miles of the location of the entity or charity.  Therefore your website would not be of any interest to someone in India, China or Russia. 

The hosting control panel has some country blocking options. You can block by country. In this case I blocked several countries including Russia from this site.  It is not a bombproof solution, there are ways around it from the attackers point of view, they could return through a VPN or some other path from the dark web. But in most cases it will work. 

In this case some 12 hours later, the server in Russia is still probing the website every minute, which just goes to prove it is a hackers program that is doing this running on a remote server, and probably probing hundreds of sites. However in our case it is blocked at the server before it reaches the website. 


IP address is now blocked from accessing the hosting

If you are affected…

If you suddenly see an uptick in spam messages, and they all seem to be related (Russian or Chinese for example) send me a message and I will check. They are a nuisance, but there are ways of stopping them, both at the hosting, preventing access to the site, and adding spam filtering if there are some common themes if you are affected by direct email.

However do not ignore it. If the spam is originating via your website contact form, this may impact your other users.  Send me a message through the contact us page if you want me to check.

Wingrove-Services
Privacy Overview

This website uses cookies so that we can provide you with the best user experience possible. Cookie information is stored in your browser and performs functions such as recognising you when you return to our website and helping our team to understand which sections of the website you find most interesting and useful.

You can adjust all of your cookie settings by navigating the tabs on the left hand side.

My privacy policy can be located here: Wingrove Media Privacy Policy (opens in a new window)

My Cookies Policy can be found here: Wingrove Media Cookies Policy (opens in a new window)